Foreign News
North Korean hackers cash out hundreds of millions from $1.5bn ByBit hack

Hackers thought to be working for the North Korean regime have successfully cashed out at least $300m (£232m) of their record-breaking $1.5bn crypto heist.
The criminals, known as Lazarus Group, swiped the huge haul of digital tokens in a hack on crypto exchange ByBit two weeks ago.
Since then, it’s been a cat-and-mouse game to track and block the hackers from successfully converting the crypto into usable cash.
Experts say the infamous hacking team is working nearly 24 hours a day – potentially funnelling the money into the regime’s military development.
“Every minute matters for the hackers who are trying to confuse the money trail and they are extremely sophisticated in what they’re doing,” says Dr Tom Robinson, co-founder of crypto investigators Elliptic.
Out of all the criminal actors involved in crypto currency, North Korea is the best at laundering crypto, Dr Robinson says.
“I imagine they have an entire room of people doing this using automated tools and years of experience. We can also see from their activity that they only take a few hours break each day, possibly working in shifts to get the crypto turned into cash.”
Elliptic’s analysis tallies with ByBit, which says that 20% of the funds have now “gone dark”, meaning it is unlikely to ever be recovered.
The US and allies accuse the North Koreans of carrying out dozens of hacks in recent years to fund the regime’s military and nuclear development.
On 21 February the criminals hacked one of ByBit’s suppliers to secretly alter the digital wallet address that 401,000 Ethereum crypto coins were being sent to.
ByBit thought it was transferring the funds to its own digital wallet, but instead sent it all to the hackers.
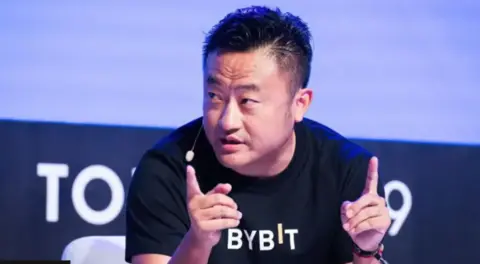
Ben Zhou, the CEO of ByBit, assured customers that none of their funds had been taken.
The firm has since replenished the stolen coins with loans from investors, but is in Zhou’s words “waging war on Lazarus”.
ByBit’s Lazarus Bounty programme is encouraging members of the public to trace the stolen funds and get them frozen where possible.
All crypto transactions are displayed on a public blockchain, so it’s possible to track the money as it’s moved around by the Lazarus Group.
If the hackers try to use a mainstream crypto service to attempt to turn the coins into normal money like dollars, the crypto coins can be frozen by the company if they think they are linked to crime.
So far 20 people have shared more than $4m in rewards for successfully identifying $40m of the stolen money and alerting crypto firms to block transfers.
But experts are downbeat about the chances of the rest of the funds being recoverable, given the North Korean expertise in hacking and laundering the money.
“North Korea is a very closed system and closed economy so they created a successful industry for hacking and laundering and they don’t care about the negative impression of cyber crime,” Dr Dorit Dor from cyber security company Check Point said.
Another problem is that not all crypto companies are as willing to help as others.
Crypto exchange eXch is being accused by ByBit and others of not stopping the criminals cashing out.
More than $90m has been successfully funnelled through this exchange.
But over email the elusive owner of eXch – Johann Roberts – disputed that.
He admits they didn’t initially stop the funds, as his company is in a long-running dispute with ByBit, and he says his team wasn’t sure the coins were definitely from the hack.
He says he is now co-operating, but argues that mainstream companies that identify crypto customers are abandoning the private and anonymous benefits of crypto currency.
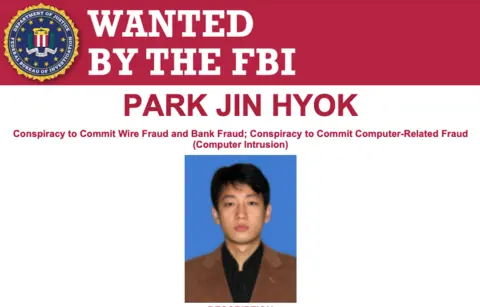
North Korea has never admitted being behind the Lazarus Group, but is thought to be the only country in the world using its hacking powers for financial gain.
Previously the Lazarus Group hackers targeted banks, but have in the last five years specialised in attacking cryptocurrency companies.
The industry is less well protected with fewer mechanisms in place to stop them laundering the funds.
Recent hacks linked to North Korea include:
- The 2019 hack on UpBit for $41m
- The $275m theft of crypto from exchange KuCoin (most of the funds were recovered)
- The 2022 Ronin Bridge attack which saw hackers make off with $600m in crypto
- Approximately $100m in crypto was stolen in an attack on Atomic Wallet in 2023
In 2020, the US added North Koreans accused of being part of the Lazarus Group to its Cyber Most Wanted list. But the chances of the individuals ever being arrested are extremely slim unless they leave their country.
[BBC]

The Philippine Coast Guard says it has recovered 41 bodies from the wreckage of a ferry that caught fire this week, bringing the total death toll to 76.
More than 130 people were on board the MV June Aster when the blaze erupted on Wednesday as it neared its destination at the tourist hotspot of Coron, after departing from Manila.
The coast guard said on Saturday the number of survivors remained 43, with many receiving treatment in hospital, but 13 people remain unaccounted for.
Recovery of bodies had been hampered due to toxic fumes and lingering heat, which meant authorities were unable to board until Friday.
Geronimo Tuvilla, an official for the Philippine Coast Guard, said the priority was identifying victims and determining the cause of the blaze.
Kristine Ablana, a tourism official in Coron, said relatives were being asked to help identify family members through personal items and DNA testing.
“Once someone is able to verify that this photo or these belongings are indeed those of their relative, they will be asked to provide a DNA sample,” she said.
Coast Guard spokesperson Commodore Noemie Cayabyab said the fire began in a cargo hold before spreading.
She said survivors had described hearing a loud explosion, “the appearance of smoke and then fire. It spread very quickly”. She added that those who had made it off the ship did not have time to put on lifejackets.
A survivor who was hauled to safety on a rescue boat told the BBC he had heard frantic cries onboard when the fire erupted, and was trampled by panicked people as he tried to escape.
The ferry, built in 2002, held valid safety certificates and passed an enforcement inspection in March, but investigators are looking into potential manifest discrepancies, cargo loading integrity, and crew emergency response protocols, the Palawan Daily reported.
The vessel was carrying 117 passengers and 17 crew members.
Atienza Interisland Ferries, the vessel’s operator, has pledged full co-operation with the inquiry.
[BBC]
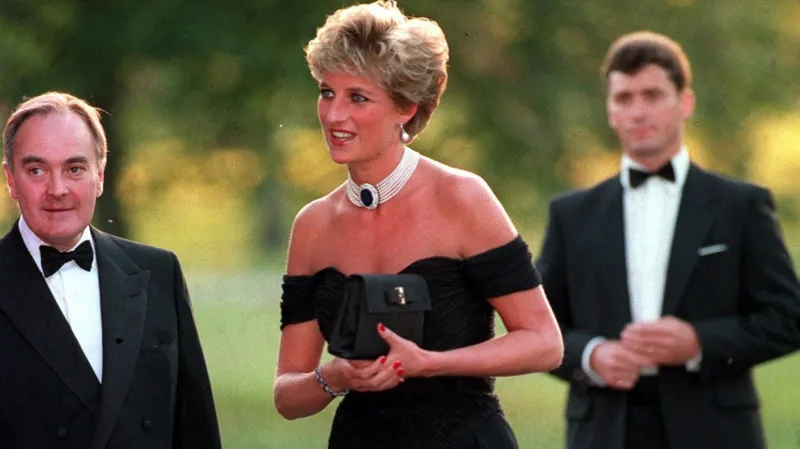
A dress worn by Princess Diana to a party in London hours after a documentary was televised in which the then-Prince Charles admitted to committing adultery during their marriage is going up for auction.
Her dramatic arrival at the Serpentine Gallery in 1994 in a custom-made black silk evening dress by designer Christina Stambolian became an iconic pop-culture moment.
The media dubbed her outfit the “revenge dress”.
Auction house Sotheby’s expects the dress to sell for up to £220,000 ($300,000) when it goes under the hammer on 9 December.
A press release from Sotheby’s said it is the first time the dress has been offered at auction since 1997, when the late princess sold 79 of her dresses to raise money for charities.
Morgane Halimi, Sotheby’s Global Head of Handbags and Fashion, said in a statement that Princess Diana “understood instinctively” that fashion can be a language in its own right.
“On her own terms, Princess Diana turned the dress into one of the most powerful messages she ever made, during one of the most scrutinised and emotionally charged episodes of her life,” Halimi said.
“She walked into a moment in which so much of her story was being told for her and, through what she chose to wear, reclaimed the narrative for herself.”

According to Sotheby’s, Anna Harvey, her stylist at the time, said Diana “wanted to look a million dollars”.
The princess made a last-minute wardrobe change for the fundraising dinner and chose the strapless evening dress by the Greek designer Christina Stambolian – which she accessorised with a royal jewel, a black clutch and black heels.
The vintage Jaguar XJ40 car that Diana arrived in at the event was sold at auction earlier this year for £66,250.
The revenge dress is expected to fetch a considerably higher price.
If it does, it will not be the first time an item from the princess’s wardrobe has sold for a significant sum.
Princess Diana’s sweater featuring a black sheep among rows of white ones was sold for £920,000 at an auction by Sotheby’s in New York in 2023.
[BBC]
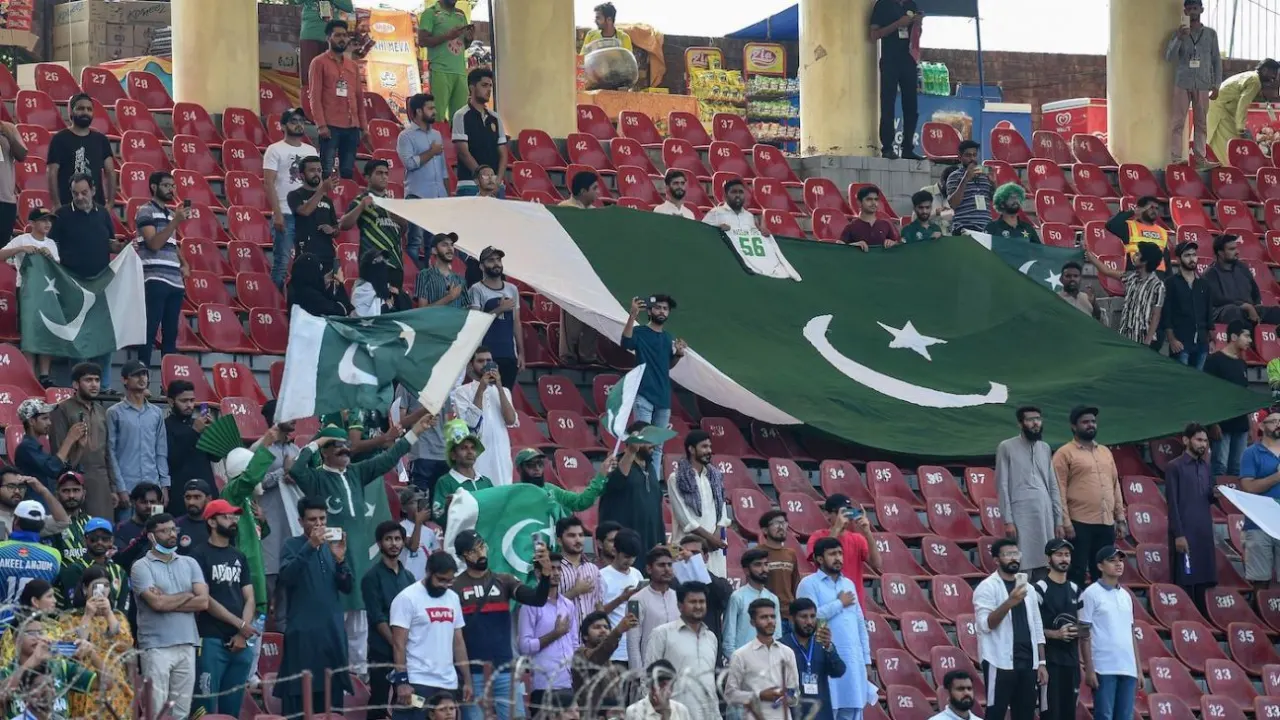
A Pakistan Under-19 cricket team suddenly became the centre of focus when it was mistaken for a group of asylum seekers in Portsmouth. A group of protesters gathered outside the Marriott Hotel in Portsmouth after reports that asylum seekers were staying there. The situation had to be later diffused when it was ascertained that the hotel was hosting the Pakistan Under-19 team.
According to the Guardian, the situation became tense when a crowd gathered outside the Marriott hotel after reports that about 40 men who did not seem to be English arrived at the hotel. George Madgwick, a Reform councillor, called the hotel to mediate between the Pakistan Under-19 staff and the assembled crowd, following which the crowd dispersed.
“I spoke to the coach of the team, who was very understanding,” Madgwick told the Guardian. “I went out to the protesters and told them, ‘You’ve got it wrong guys, it’s a cricket club.’ They left within a couple of minutes. It was a massively unfortunate incident.
“From the perspective of the people of Portsmouth who are already on high alert, this was a coach from the same company which was turning up with about 40 foreign men.”
The ECB has been in touch with the Pakistan management following the incident and is reviewing security arrangements.
The Pakistan Under-19 team played a four-day game against England Under-19 in Arundel from September 2 to 5, which they lost by ten runs. The two teams faced off in a Youth ODI on September 9, with Pakistan winning by 177 runs. Pakistan’s senior men’s team are also playing the third and final Test against England at Edgbaston.
[Cricinfo]

Showers in most parts of the island today (17)

US embassy won’t comment on IGP’s probe into joint drug raid

Gnanasara Thera declares outside High Court that he wouldn’t flee

Namal further remanded

22A: LAWASIA questions compostion of five-judge bench

Sri Lanka’s lifestyle coffee culture boom and the two faces of its economy

‘Dates have the highest sugar content to fight Coronavirus’

Sunday Island 27 December – Headlines

#SundayIsland 17th December – Headlines

Sunday Island – 28th March

Sunday Island Headlines – 21 March

Sunday Island – 21st February – Headlines
-

 Sports6 days ago
DDS set to lose Test captaincy
-
 News6 days ago
Sri Lanka faces new grid challenge as rooftop solar surges: former CEB GM
-
 Latest News6 days ago
Shafali, Deepti power India into sixth T20 Asia Cup final
-

 News4 days ago
Gnanasara Thero absconding after SC ruling
-
 Latest News5 days ago
Sri Lanka thwart Fatima Sana challenge to secure Asia Cup final spot
-

 News5 days ago
Ammunition cache found in old Kandy bungalow
-
 Editorial6 days ago
A flight of fancy
-

 News5 days ago
Green Climate Fund (GCF) Regional Dialogue for East and South Asia will be held from 14 to 17 September 2026 at Cinnamon Life at City of Dreams Hotel, Colombo